English

Resources

LLM Exploit Generation Guide 2.0

The GenAI Security Project’s LLM Exploit Generation Phase 2 report compares human-guided and autonomous AI approaches against live cybersecurity targets. It examines success, human effort, cost, guardrails, and operational limitations. Both approaches reduced the expertise needed for attacks, but neither eliminated it. Autonomous agents often produced noisy, repetitive activity, while human-guided attacks could be quieter. […]

LLM Exploit Generation Guide 2.0 Read Post »
Resources

GenAI Red Teaming Manual Version 1.0

The GenAI Security Project’s GenAI Red Teaming Manual provides practical guidance for evaluating the security, safety, and robustness of generative AI systems. Its eight-phase methodology covers planning, reconnaissance, attack surface mapping, exploitation, persistence, impact assessment, reporting, and remediation. Addressing models, applications, multimodal interfaces, and AI agents, it emphasizes ethical testing, reproducible findings, measurable outcomes, and

GenAI Red Teaming Manual Version 1.0 Read Post »

Resources

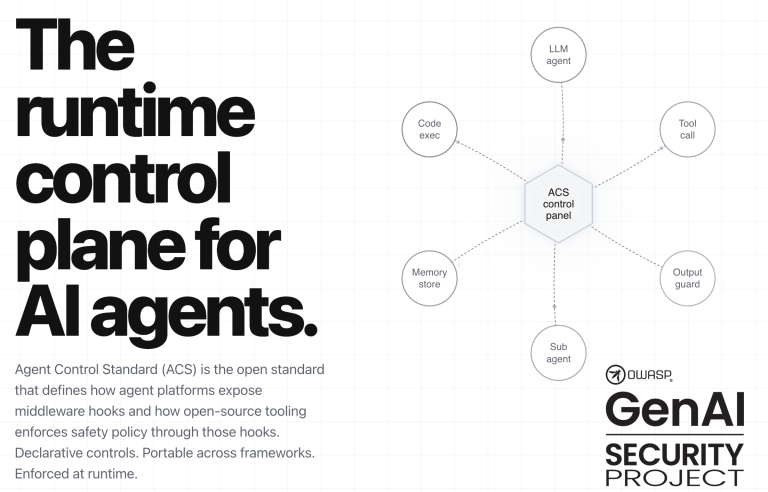
Agent Control Standard (ACS)

Widescale adoption of AI agents depends on trust, and trust requires transparency and control. Enterprises cannot rely on black-box agents operating across cloud, SaaS, on-premises and endpoint environments. Agents must be inspectable, traceable and instrumentable—providing visibility into what they are, what they can access, what they did and why, and the ability to control their

Agent Control Standard (ACS) Read Post »

Resources

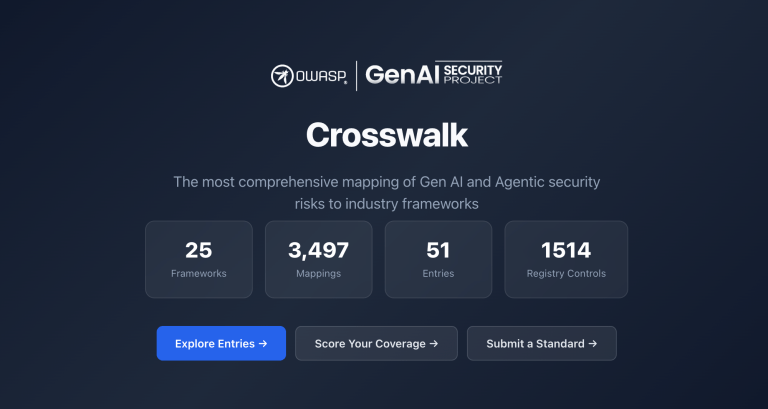
GenAI Security Industry Framework Crosswalk

The OWASP GenAI Security Project Crosswalk is an open-source resource that connects OWASP GenAI security risks to established industry security, governance, and compliance frameworks. It maps 51 GenAI vulnerabilities across four  source lists to controls in 25 frameworks, including NIST, ISO, MITRE ATLAS, the EU AI Act and others. Organizations can use the crosswalk to

GenAI Security Industry Framework Crosswalk Read Post »

Resources

OWASP GenAI LLM Top 10 2026

OWASP Top 10 for LLM Applications 2026 is the latest community-driven guide to the most critical security risks facing applications powered by large language models. Developed by hundreds of AI security experts, this edition introduces updated rankings, expanded threat coverage, and new research grounded in thousands of real-world AI security incidents. The guide provides practical

OWASP GenAI LLM Top 10 2026 Read Post »

Resources

Solutions Landscape – Red Teaming Taxonomy

  This document serves as the foundational taxonomy for the AI and Agentic Red Teaming Solutions Guide. It establishes a common language and structured classification of capabilities across red, blue, and purple teaming, organized by practitioner lifecycle stages. The taxonomy is intended to support companion solutions guides and cheat sheets that map, in detail, how

Solutions Landscape – Red Teaming Taxonomy Read Post »

Resources

State of Agentic AI Security and Governance 2.01

The State of Agentic AI Security and Governance provides a comprehensive view of today’s landscape for securing and governing autonomous AI systems. It explores the frameworks, governance models, and global regulatory standards shaping responsible Agentic AI adoption. Designed for developers, security professionals, and decision-makers, the report serves as a practical guide for navigating the complexities

State of Agentic AI Security and Governance 2.01 Read Post »

Resources

AIUC-1: Crosswalks OWASP Top 10 For Agentic Applications

The AIUC-1 Crosswalk of the OWASP Top 10 for Agentic Applications provides a bidirectional mapping between AIUC-1 requirements and the OWASP Agentic Security Initiative’s Top 10 risks for autonomous and agentic AI systems. It helps organizations understand how AIUC-1 controls align with threats such as agent goal hijacking, tool misuse, identity and privilege abuse, memory

AIUC-1: Crosswalks OWASP Top 10 For Agentic Applications Read Post »

Resources

AI Security Solutions Landscape For AI and Agentic Red Teaming Q2 2026

As organizations increasingly deploy generative AI and autonomous agents into business-critical workflows, traditional application security practices are no longer sufficient. AI systems introduce new classes of risk including prompt injection, model misuse, agent privilege escalation, data poisoning, hallucinations, and emergent behaviors that evolve continuously throughout the AI adoption lifecycle. Gen AI and Agentic Red Teaming

AI Security Solutions Landscape For AI and Agentic Red Teaming Q2 2026 Read Post »

Resources

AI Security Solutions Landscape for Agentic AI Q2 2026

The Solutions Landscape monitors and maps the full Agentic AI lifecycle, focusing on the DevOps–SecOps intersection to meet evolving security needs. Guided by the Agentic AI Threats and Mitigations guide and SecOps tasks, it highlights open-source and commercial solutions by stage, identifying their coverage of Agentic SecOps duties and threat mitigation, and leverages industry and

AI Security Solutions Landscape for Agentic AI Q2 2026 Read Post »

Ask Sage, GenAI Security Advisor
Scroll to Top

AI Security Solutions Landscape for Agentic AI Q2 2026